Carmen Young ✳
About me

A note from me

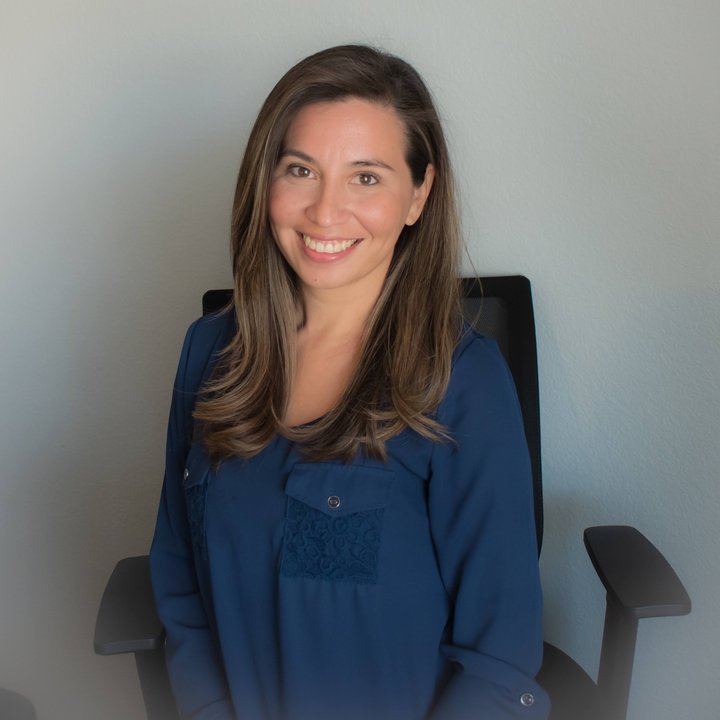
Portrait of Carmen Young

Hi there! I'm glad you're here. I am not on any social media, but I wanted a place to showcase my work and my experience.

I've been in the industry for close to 10 years now, and I'm still enjoying the journey.

My approach is built on a simple belief: in this industry, relationships are the real infrastructure. That philosophy has shaped my career and is the thread running through everything I do today.

Scroll down and see what I've worked on and what I'm working on. And if you'd like, reach out! I'd love to hear from you.

With warmth,

Carmen

My Experience

01

Improved incident response speed and efficiency by implementing a new process with defined escalation protocols, a structured escalation matrix, and cross-team collaboration.

02

Strengthened organizational preparedness by developing realistic tabletop scenarios that improved coordination across teams and validated incident response strategies.

2026 — Present

Technical Cyber Security Program Manager

Undisclosed· Remote

Details on this role are available on request.
2018 — 2025

Sr. Cyber Security Engineer

Staples, Inc. · Remote

  • Lead end-to-end response to cyber incidents, coordinating cross-functional teams to timely resolution with minimal operational impact — serving as the primary liaison between technical teams, legal, and communications during high-pressure events.
  • Authored the Incident Response Plan, aligned with industry standards and regulatory requirements, and own its full lifecycle — continuously improving it with lessons learned from tabletop exercises and real incidents.
  • Directed penetration testing initiatives for PCI compliance, acting as liaison between compliance teams, internal stakeholders, and external vendors to drive prompt remediation.
  • Designed and facilitated technical tabletop exercises with realistic incident scenarios, validating remediation steps and strengthening team preparedness.
  • Played a hands-on role in the SIEM Platform deployment, including detection engineering rules and coordination of technical priorities with stakeholders.
  • Orchestrated the rollout of GRC modules suc as Vendor Risk Management, Risk Register, Policy Exception — and administered the ServiceNow SOC module, streamlining compliance workflows and threat management.
  • Championed process documentation, maintaining internal playbooks and knowledge bases for consistent, scalable response operations.
2009 — 2018

Project Analyst / IT Contracts Manager

SPAWARSYSCEN PACIFIC · Colorado Springs, CO & San Diego, CA

  • Provided Program Analyst and Information Assurance support for J6 Command and Control at NORAD-NORTHCOM — reviewing security controls under the Risk Management Framework and ensuring STIG compliance through the Principal Network Node project's installation and implementation.
  • Served as the main point of contact for information assurance matters between the PNN project and the J6 IA team.
  • Oversaw two single-award contracts totaling over $107M, supported RFPs for two Multiple Award Contracts, and helped get more than 60 task orders awarded on schedule.
  • Designed a relational database tracking all contract information with customizable funding reports, plus a finance form that streamlined the division's workflows.
  • Delivered monthly financial analysis of labor, travel, and material expenditures to upper management, and partnered with leadership to solve procedural problems before they grew.

Education & credentials

Degree
Bachelor's, Information Technology Management
Certification
Certified in Cybersecurity (CC) — (ISC)² · Threat Intelligence Support Unit (TISU)
Training
SEC401: Security Essentials (SANS Institute) · Security Auditing & Penetration Testing (CU Boulder) · Digital Forensics (CU Boulder) · Black Hat USA Associate Program 2025 and 2026
Tools
ServiceNow · LogicGate · Microsoft Sentinel
Reach out →